
Mature & respond
NIST Cybersecurity Framework
Use NIST CSF 2.0 to measure maturity, set a target profile, and communicate cyber risk in terms the board understands.
Overview
The NIST Cybersecurity Framework is a flexible, outcome-based framework used worldwide. Version 2.0 organises security into six functions: Govern, Identify, Protect, Detect, Respond and Recover.
It is especially useful for organisations with US customers or investors, or anyone wanting a maturity model that goes beyond a pass/fail certificate.
Ideal for
- Organisations with US customers, parents or investors
- Security programmes wanting a maturity model
- Boards wanting clear, comparable cyber reporting
What's included
Scope of the service
Current profile
Assess current outcomes across all six CSF 2.0 functions.
Target profile
Agree realistic target maturity based on your risk and objectives.
Govern function
Strengthen cyber risk strategy, roles and oversight.
Heat map
A clear visual of strengths and gaps for leadership.
Roadmap
Prioritised actions to move from current to target profile.
Framework mapping
Map CSF to ISO 27001 or Cyber Essentials to avoid duplicated effort.
How it works
A clear, practical process
- 01
Frame
Agree scope, risk appetite and business objectives.
- 02
Assess
Build the current profile through interviews and evidence.
- 03
Target
Define the target profile with leadership.
- 04
Mature
Deliver a roadmap and track progress over time.
Outcomes
What you can expect
- A shared language for cyber risk across the business
- Clear, measurable maturity targets
- Better board-level reporting
- Alignment with other standards you already hold
Frequently asked questions
Is NIST CSF a certification?
No. NIST CSF is a voluntary framework, not a certifiable standard. It is often used alongside ISO 27001 to measure and communicate maturity.
What changed in NIST CSF 2.0?
Version 2.0 added the Govern function, broadened the framework's applicability beyond critical infrastructure, and improved guidance on supply chain risk.
Related services
You may also need
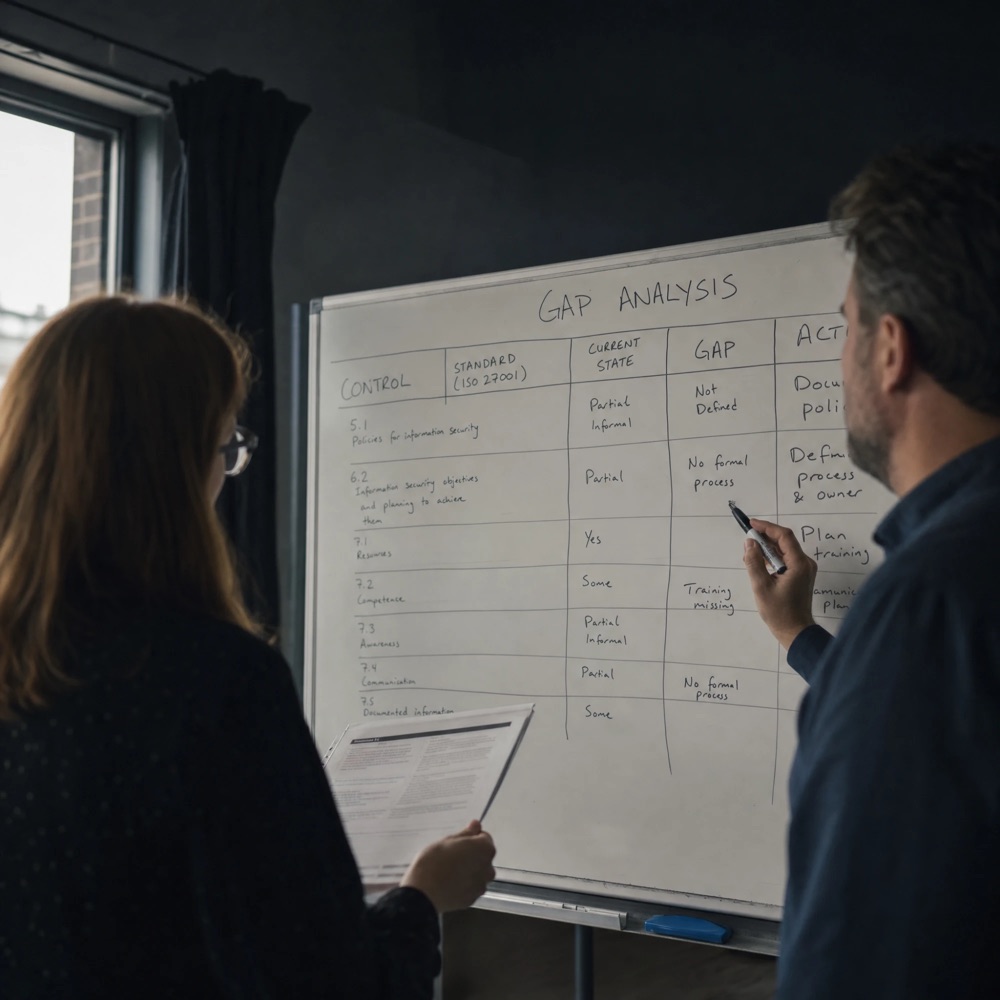
Gap Analysis
Understand exactly where you stand against a standard or framework, and what to fix first.
Learn more
NCSC Cyber Assessment Framework
Assess and build resilience against the NCSC CAF's four objectives and fourteen principles.
Learn more
Virtual CISO
Strategic security leadership without the cost of a full-time Chief Information Security Officer.
Learn moreLet's talk
Start your journey to a more secure tomorrow.
A free, no-obligation 30-minute discovery call to understand your goals and suggest the most practical next step.