
Cyber Essentials or ISO 27001: where should you start?
Two very different certifications. Here's how to decide which one delivers the most value first.
Independent information security consultancy
Helping organisations build stronger, more resilient futures, from Cyber Essentials Plus and ISO 27001 to virtual CISO leadership and incident readiness.
ISO 27001 and Cyber Essentials Plus, from first gap analysis through to a successful audit.
Certification services
A virtual CISO to set strategy, own risk and report to your board, without a full-time hire.
Virtual CISO
Response plans, playbooks and tabletop exercises, so your team knows exactly what to do.
Incident readiness
Check your organisation against all five controls before you apply for certification.
Get the checklistServices
From your first gap analysis to certification and beyond: practical, independent advice tailored to your organisation.
Secure
Senior security leadership, clear policy and risk decisions you can defend.
Strategic security leadership without the cost of a full-time Chief Information Security Officer.
Learn more
Clear, practical policies, standards and procedures that people can actually follow.
Learn more
Make informed security decisions with risk assessments, registers and treatment plans.
Learn moreComply
Achieve and maintain the standards your customers, insurers and regulators expect.
Implement, certify and maintain an ISMS that works for your business, not just for the auditor.
Learn more
Demonstrate your security fundamentals with readiness reviews and hands-on support through certification.
Learn more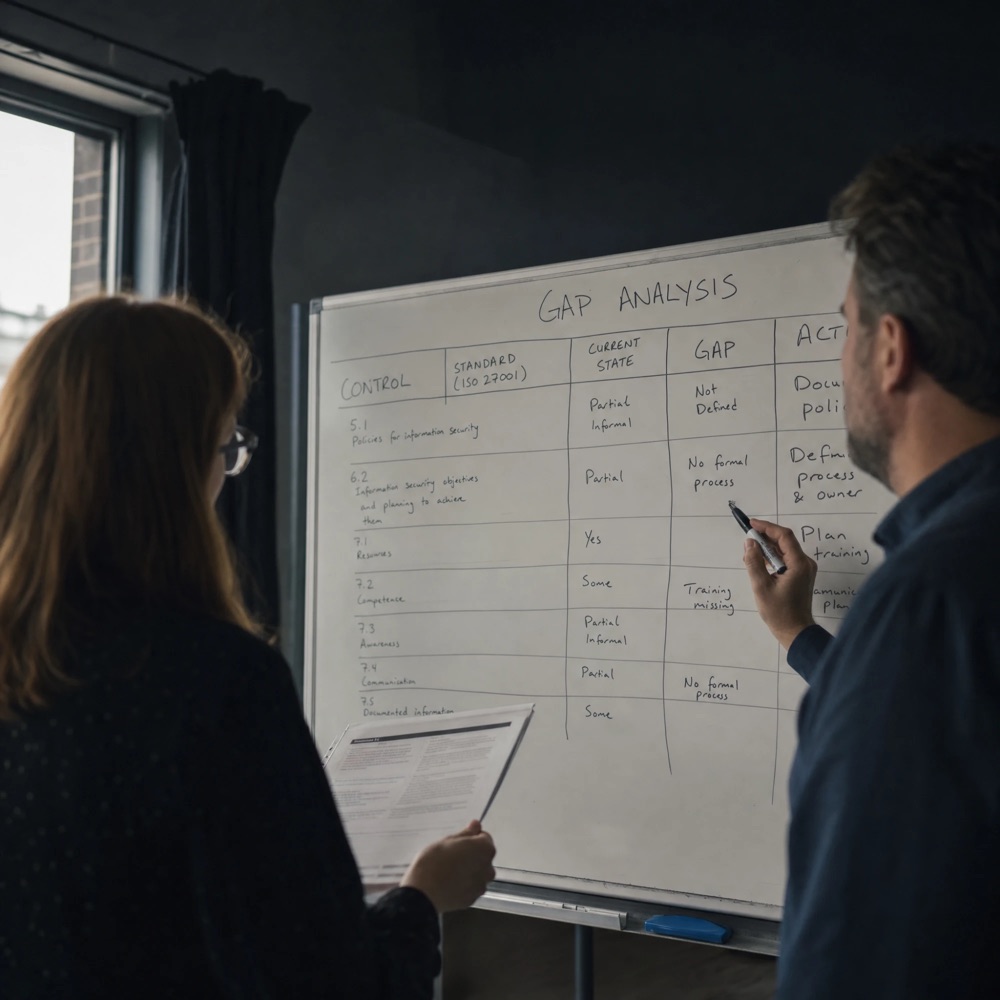
Understand exactly where you stand against a standard or framework, and what to fix first.
Learn more
Assess and build resilience against the NCSC CAF's four objectives and fourteen principles.
Learn moreProgress
Measure and grow your security maturity, plan for the worst, rehearse your response and build a security-aware culture.
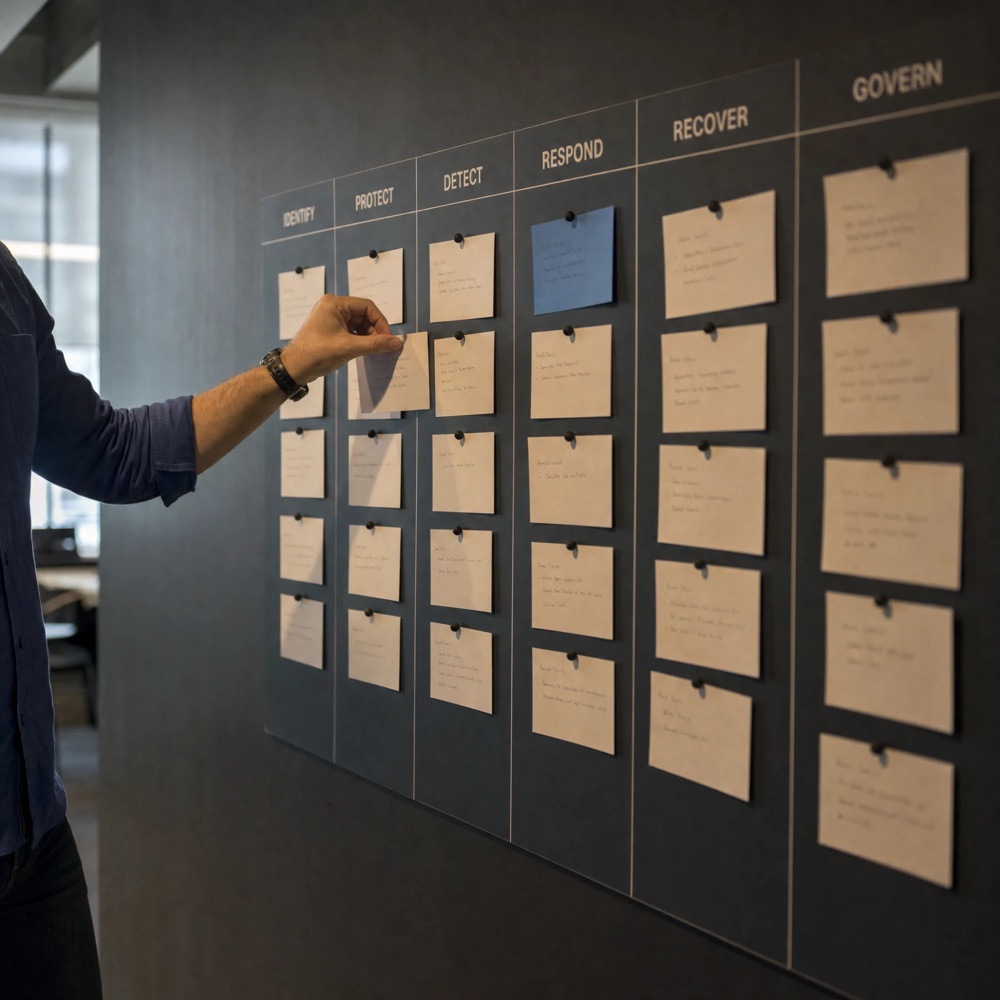
Align and mature your security programme with NIST CSF 2.0's six core functions.
Learn moreBe ready before the incident happens, with clear plans, playbooks and communication.
Learn more
Test your response before it matters, with realistic scenarios for technical teams and executives.
Learn more
Build a security-aware culture with engaging training for staff, executives and boards.
Learn moreYour security journey
Whatever standard you're working towards, the route to the top follows the same five steps. Each one builds on the last, so your investment compounds instead of starting over.
Understand where you stand today and where the real risks are.
Agree a practical, risk-based roadmap with clear owners and timescales.
Put the right policies, controls and processes in place.
Prove it works through audits, testing and tabletop exercises.
Keep improving with ongoing leadership, reviews and reporting.
Assess Plan Implement Test Improve
Why McArthur Infosec
Security succeeds when everything works together. I look at the whole picture, not just the technology, so the improvements you make actually last.
Skilled, aware and empowered teams, from the board to the front line.
Clear, consistent and effective policies, risk management and governance.
Secure, resilient and well-managed systems, aligned to recognised standards.
Insights
Two very different certifications. Here's how to decide which one delivers the most value first.
Senior security leadership without a full-time hire. What to expect, and when it makes sense.
The cheapest way to find out whether your incident response plan really works.
Free resource
A practical checklist covering all five Cyber Essentials control themes. Find your gaps before the assessor does.
Usually with a short discovery call, followed by a gap analysis. This shows where you stand today and which standard or service will give you the most value first.
Cyber Essentials is a verified self-assessment of five technical controls. Cyber Essentials Plus covers the same controls but adds a hands-on technical audit by an independent assessor.
Typically 6–12 months from gap analysis to certification, depending on the scope and how mature your existing security practices are.
No, and that is deliberate. Certification is carried out by independent certification bodies. I prepare you and support you through the audit, so the advice you receive stays independent.
A virtual CISO provides senior security leadership on a part-time basis: setting strategy, owning risk, guiding your IT team or provider, and reporting to the board.
Both. Most work can be delivered remotely, with on-site workshops, audits and tabletop exercises where they add value.
Let's talk
A free, no-obligation 30-minute discovery call to understand your goals and suggest the most practical next step.