
Certify & comply
NCSC Cyber Assessment Framework
Assess. Improve. Build resilience. Practical support against all four CAF objectives.
Overview
The NCSC Cyber Assessment Framework (CAF) is used across UK essential services, the public sector and their suppliers to assess cyber resilience.
It is structured around four objectives (managing security risk, protecting against cyber attack, detecting cyber security events, and minimising the impact of incidents) and fourteen principles.
Ideal for
- Operators of essential services and their suppliers
- Public sector and NHS-related organisations
- Organisations preparing for regulator scrutiny
What's included
Scope of the service
Objective A
Managing security risk: governance, risk management, asset management and supply chain.
Objective B
Protecting against cyber attack: policies, identity, data, systems and staff awareness.
Objective C
Detecting cyber security events: monitoring and proactive discovery.
Objective D
Minimising impact: response and recovery planning and lessons learned.
Outcome ratings
Evidence-based ratings for each contributing outcome.
Improvement plan
Practical, prioritised actions for areas not yet achieved.
How it works
A clear, practical process
- 01
Scope
Identify essential functions and supporting systems.
- 02
Assess
Evidence-based assessment against each principle.
- 03
Prioritise
Agree improvements based on risk and impact.
- 04
Improve
Support delivery and reassessment.
Outcomes
What you can expect
- A defensible position for regulators and customers
- Clear understanding of operational resilience
- Targeted, risk-based investment
- Better detection and response capability
Frequently asked questions
Who needs to use the CAF?
It is primarily used by operators of essential services under the NIS Regulations, parts of the public sector and their suppliers, but any organisation can use it to assess resilience.
Is the CAF a certification?
No. The CAF is an assessment framework rather than a certificate. The result is a set of evidence-based outcome ratings and an improvement plan you can share with regulators, customers or your board.
Related services
You may also need
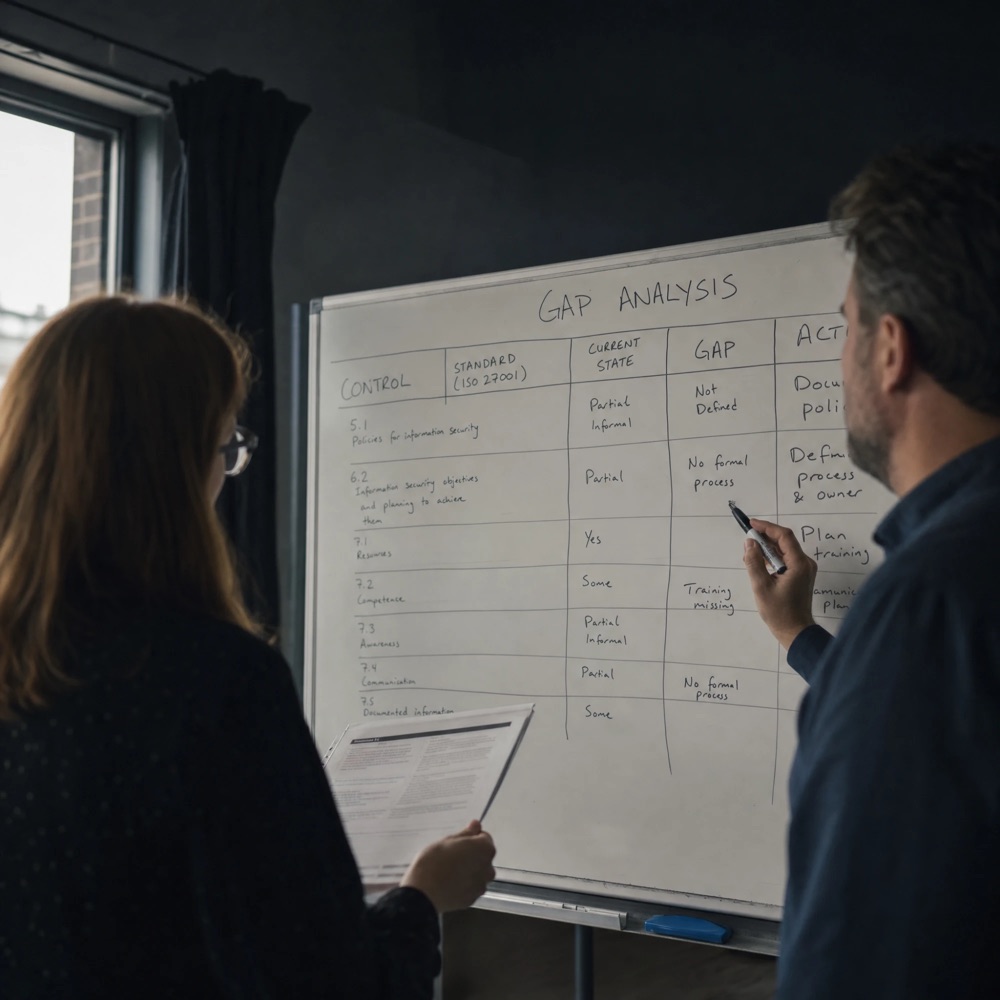
Gap Analysis
Understand exactly where you stand against a standard or framework, and what to fix first.
Learn more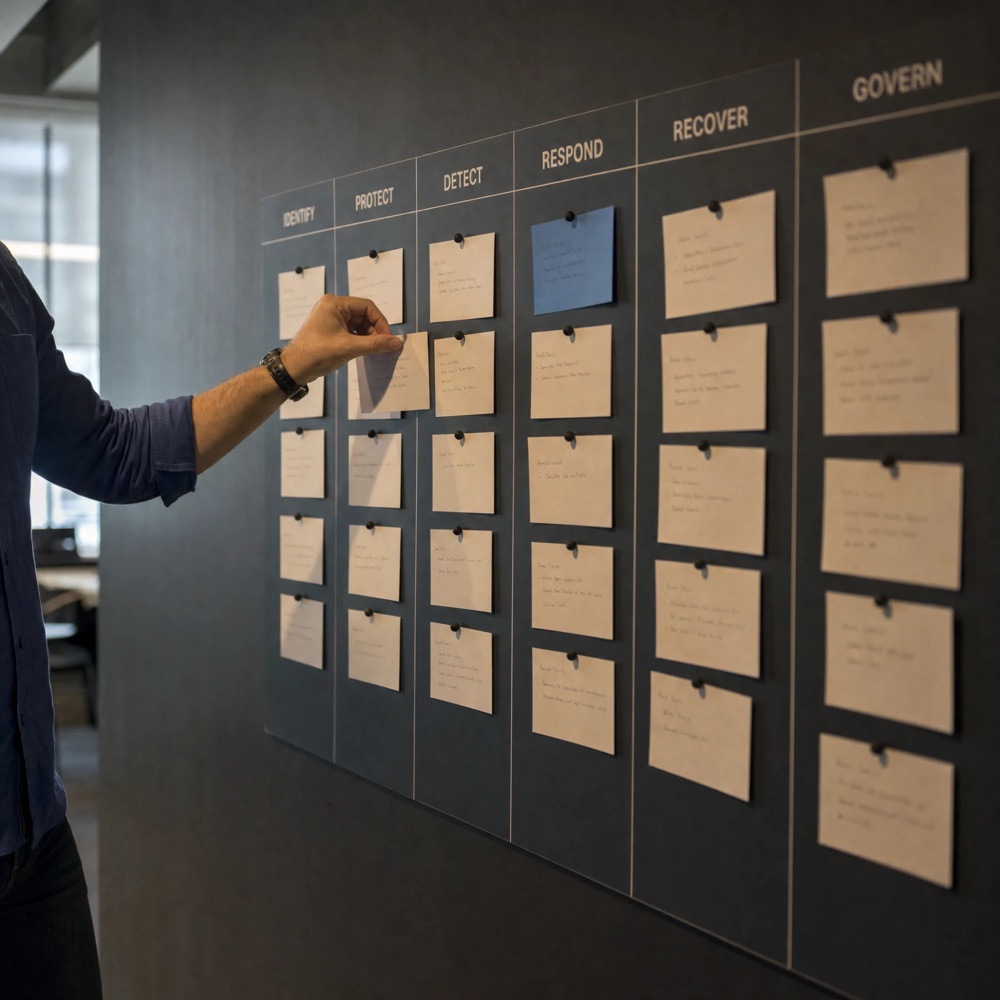
NIST Cybersecurity Framework
Align and mature your security programme with NIST CSF 2.0's six core functions.
Learn more
Incident Response Planning
Be ready before the incident happens, with clear plans, playbooks and communication.
Learn moreLet's talk
Start your journey to a more secure tomorrow.
A free, no-obligation 30-minute discovery call to understand your goals and suggest the most practical next step.