
Certify & comply
Gap Analysis
A clear, honest picture of your current security posture, with a prioritised roadmap to where you need to be.
Overview
A gap analysis compares how you operate today with the requirements of a chosen standard or framework, such as ISO 27001, Cyber Essentials, NIST CSF or the NCSC CAF.
You get a plain-English report that shows what is working, what is missing, and a realistic, prioritised plan to close the gaps.
Ideal for
- Organisations starting a certification journey
- Leadership teams needing an independent view of security
- Businesses preparing for a customer or regulatory audit
What's included
Scope of the service
Stakeholder interviews
Short, focused conversations with the people who run your systems and processes.
Evidence review
Review of existing policies, records and technical configuration.
Maturity scoring
Scoring against each requirement so progress can be measured over time.
Risk-based priorities
Gaps ranked by risk and effort, not just listed.
Roadmap
A phased plan with quick wins and longer-term improvements.
Board summary
An executive-level summary to support decisions and budget.
How it works
A clear, practical process
- 01
Scope
Agree the framework, scope and stakeholders.
- 02
Discover
Interviews, document review and technical sampling.
- 03
Analyse
Score maturity and assess the risk of each gap.
- 04
Report
Present findings and a prioritised roadmap.
Outcomes
What you can expect
- An independent, evidence-based baseline
- Clear priorities and realistic timelines
- A business case for security investment
- A measurable starting point for improvement
Frequently asked questions
Which frameworks can you assess against?
Commonly ISO/IEC 27001:2022, Cyber Essentials, NIST CSF 2.0 and the NCSC Cyber Assessment Framework. Other frameworks can be covered on request.
Will the gap analysis disrupt my team?
No. Interviews are short and scheduled around your team, and existing documents are reused wherever possible.
Related services
You may also need
ISO 27001 Consultancy
Implement, certify and maintain an ISMS that works for your business, not just for the auditor.
Learn more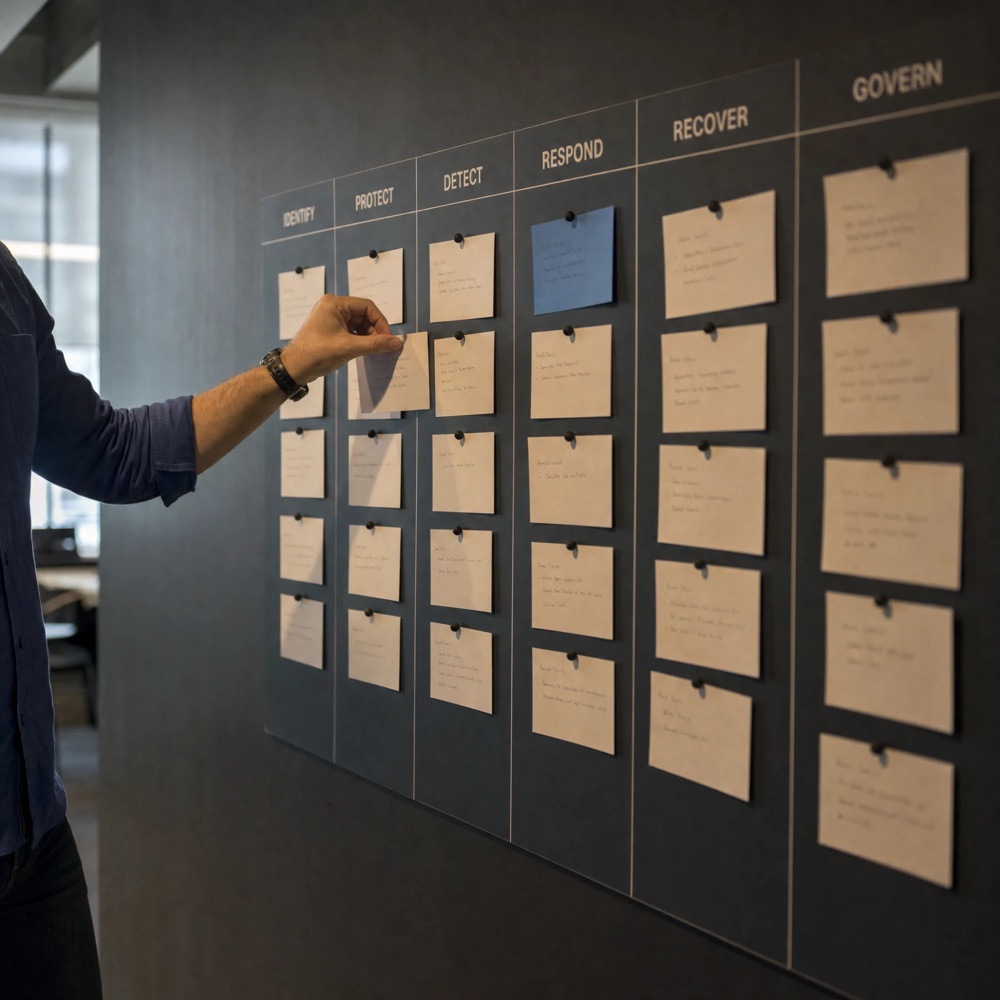
NIST Cybersecurity Framework
Align and mature your security programme with NIST CSF 2.0's six core functions.
Learn more
NCSC Cyber Assessment Framework
Assess and build resilience against the NCSC CAF's four objectives and fourteen principles.
Learn moreLet's talk
Start your journey to a more secure tomorrow.
A free, no-obligation 30-minute discovery call to understand your goals and suggest the most practical next step.