
Certify & comply
ISO 27001 Consultancy
A practical route to ISO/IEC 27001:2022 certification, with an information security management system your team will actually use.
Overview
ISO/IEC 27001 is the internationally recognised standard for information security management. Certification shows customers, partners and tenders that you manage information risk in a structured, audited way.
I help you scope the ISMS sensibly, build only the documentation you need, and embed controls into how you already work, so certification is the start of better security rather than a paperwork exercise.
Ideal for
- Organisations responding to customer or tender requirements
- Businesses handling sensitive client or personal data
- Teams moving from ISO 27001:2013 or an informal approach
What's included
Scope of the service
Gap analysis
Assess your current position against clauses 4–10 and the 93 Annex A controls.
ISMS scoping
Define a scope that meets your commercial goals without unnecessary overhead.
Risk assessment
Identify, evaluate and treat information security risks with a repeatable method.
Documentation
Right-sized policies, procedures and Statement of Applicability.
Internal audit
An independent internal audit and management review before certification.
Certification support
Preparation for, and support through, Stage 1 and Stage 2 audits.
How it works
A clear, practical process
- 01
Assess
Gap analysis and scoping workshop to understand where you are today.
- 02
Plan
A prioritised roadmap with clear owners, timelines and effort.
- 03
Implement
Build the ISMS, deliver risk assessment and embed controls.
- 04
Certify & improve
Internal audit, certification support and continual improvement.
Outcomes
What you can expect
- Certification-ready ISMS aligned to ISO/IEC 27001:2022
- Stronger position in tenders and supplier questionnaires
- Clear ownership of information security risk
- A system that is maintainable after certification
Frequently asked questions
Do you issue the ISO 27001 certificate?
No. Certification must be carried out by an independent certification body, ideally UKAS-accredited. I prepare you for the audit and support you through it, which keeps the advice independent.
How long does ISO 27001 take?
Most organisations take 6–12 months from gap analysis to certification. Smaller scopes with existing good practice can move faster.
Can you maintain the ISMS after certification?
Yes. Ongoing support can cover internal audits, management reviews and surveillance audit preparation, often as part of a virtual CISO arrangement.
Related services
You may also need
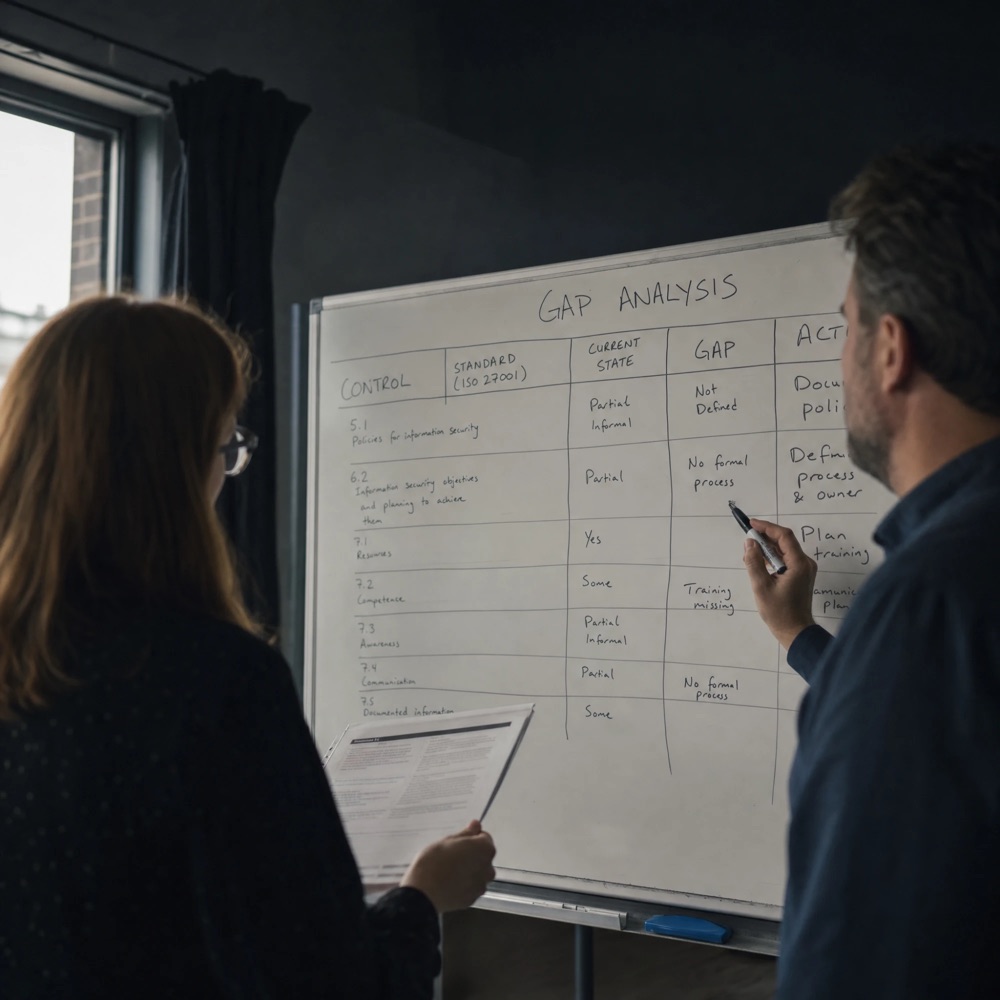
Gap Analysis
Understand exactly where you stand against a standard or framework, and what to fix first.
Learn more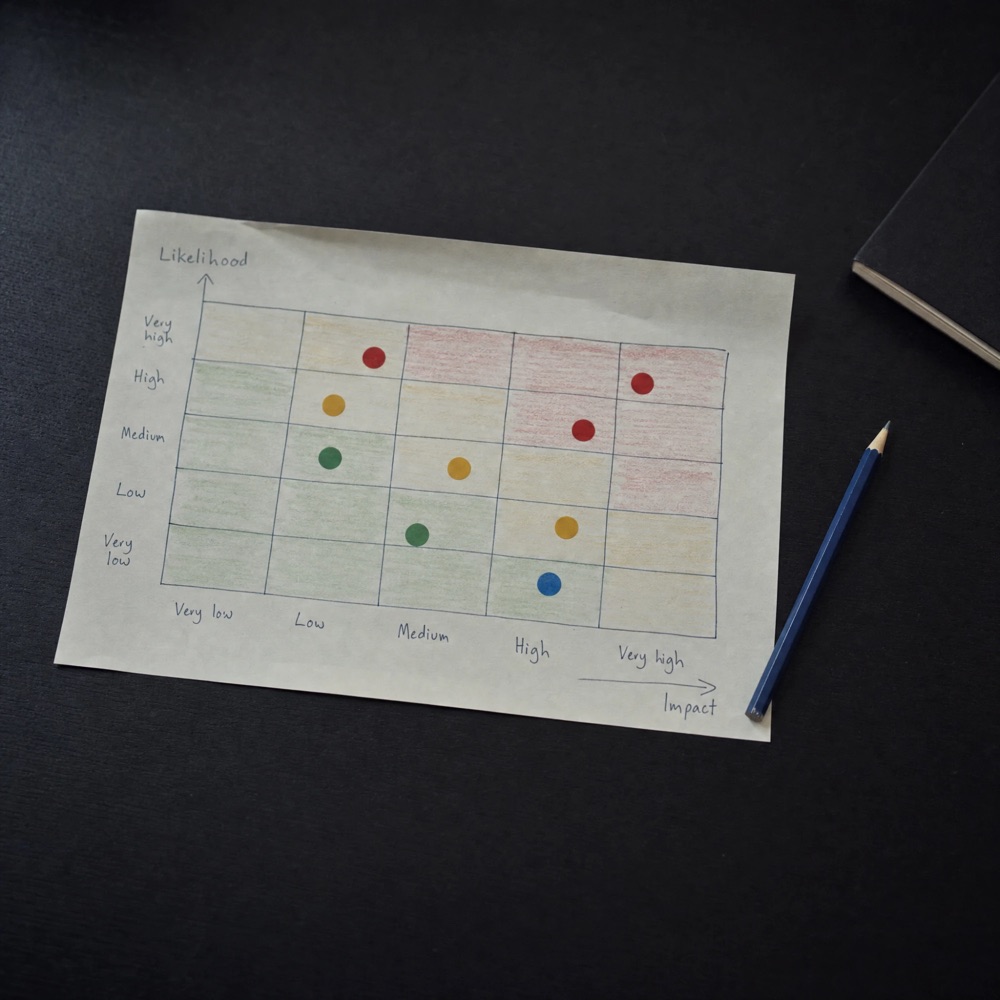
Risk Management
Make informed security decisions with risk assessments, registers and treatment plans.
Learn more
Security Policy & Governance
Clear, practical policies, standards and procedures that people can actually follow.
Learn moreLet's talk
Start your journey to a more secure tomorrow.
A free, no-obligation 30-minute discovery call to understand your goals and suggest the most practical next step.